AI governance, written plainly.
The EU AI Act, staff AI literacy, and what a verifiable training record actually is. Published here first, then shared elsewhere.
 Behind the scenes· · 4 min read
How the Academy works: the 90-second tour
A cited question bank, role tracks, a tutor grounded in the course corpus, a deterministic exam, and a record a stranger can open. Five stages, no algorithms.
By Lindsay Hiebert, CISSP→ Primer· · 5 min read
A certificate says who attended. It cannot tell you who is competent.
A certificate records attendance. It cannot show competence, and it cannot be checked by anyone who was not there. What a verifiable record has to contain.
By Lindsay Hiebert, CISSP→ Buyer's standard· · 7 min read
The AI Literacy Program Standard: the questions to ask before you buy or assign one
The questions to ask any AI-literacy program before you buy or assign it. Names no vendor, ranks nothing, and scores the Academy against it too.
By Lindsay Hiebert, CISSP→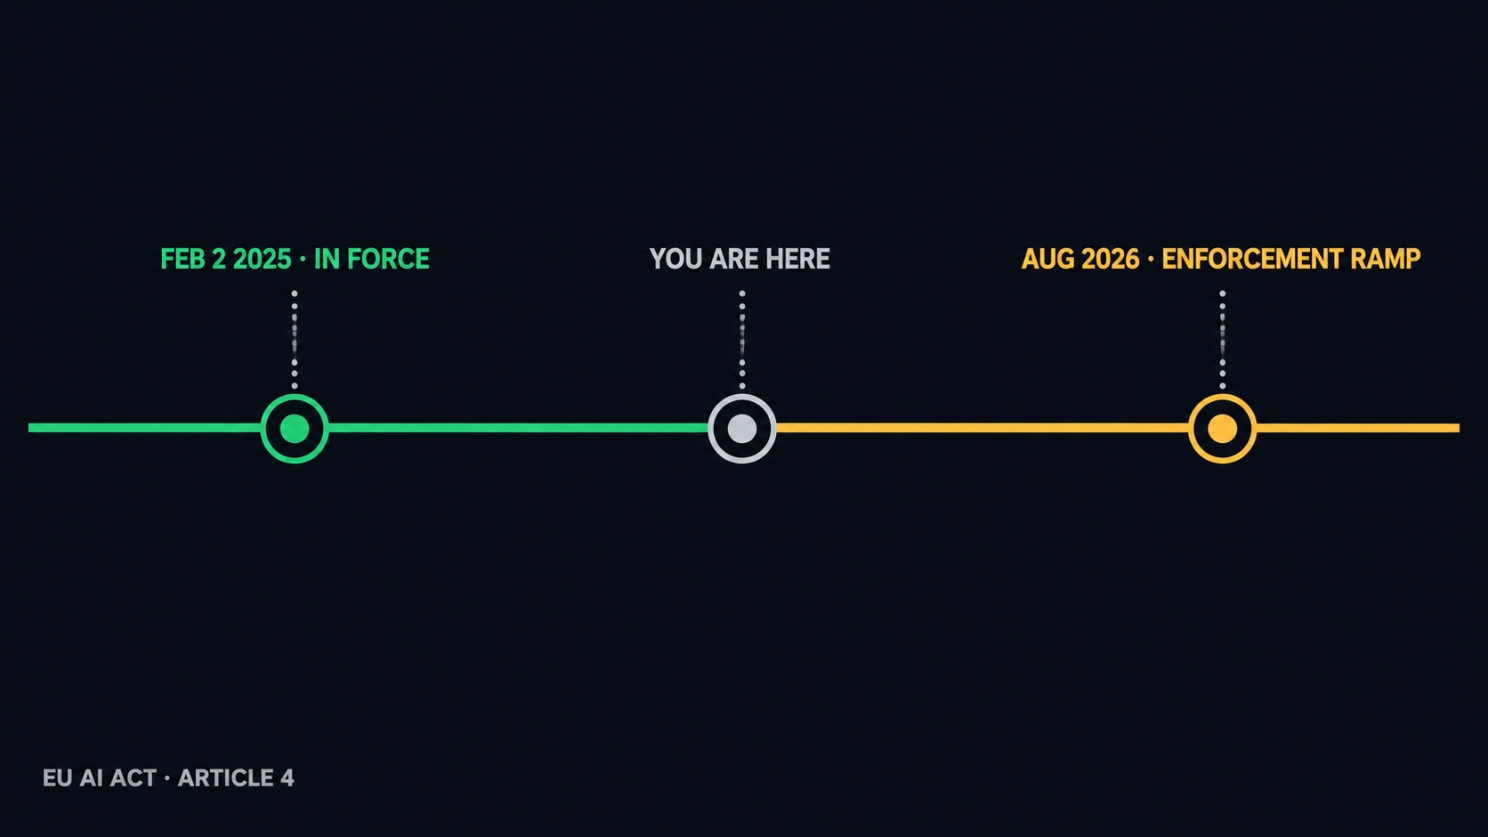 Literacy· · 6 min readOn sanctumshield.com ↗
Most people who say they have AI governance name a tool
Ask a room of security leaders whether they have AI governance and most say yes. Ask what governance is and most name a tool. Includes a ten-question literacy quiz drawn from the Academy field guide.
By Lindsay Hiebert, CISSP→- Article 4· · 7 min read
The AI training law already in effect
EU AI Act Article 4 has applied since 2 February 2025. How to credential a whole staff, role by role, with a verifiable record for each person. Written to the 2024 text of Article 4.
By Lindsay Hiebert, CISSP→
How we write.
Every regulatory statement names the article or section it rests on. We publish no pass rates or outcome figures, ours or anyone’s, and we name no vendor. Where we describe what a program should do, we say how the Academy measures against it, including where it falls short. Every count is rendered from the product at build time, never typed. The canonical copy of every piece lives here; copies elsewhere link back.